Description
“I banned this person. They came back with a new email.”
You block a customer who charged back or abused your store. A week later the same person orders again, with a new email, a slightly different phone number and the same apartment. WooCommerce sees a brand new customer. So do you, until the dispute lands.
What it does
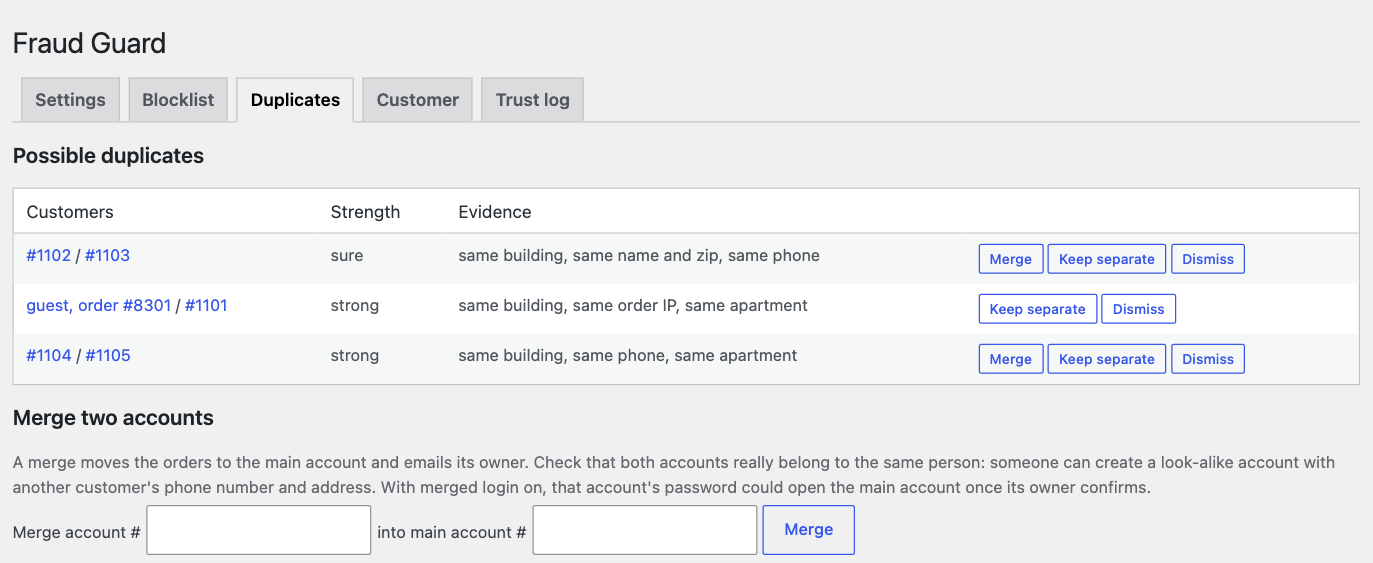
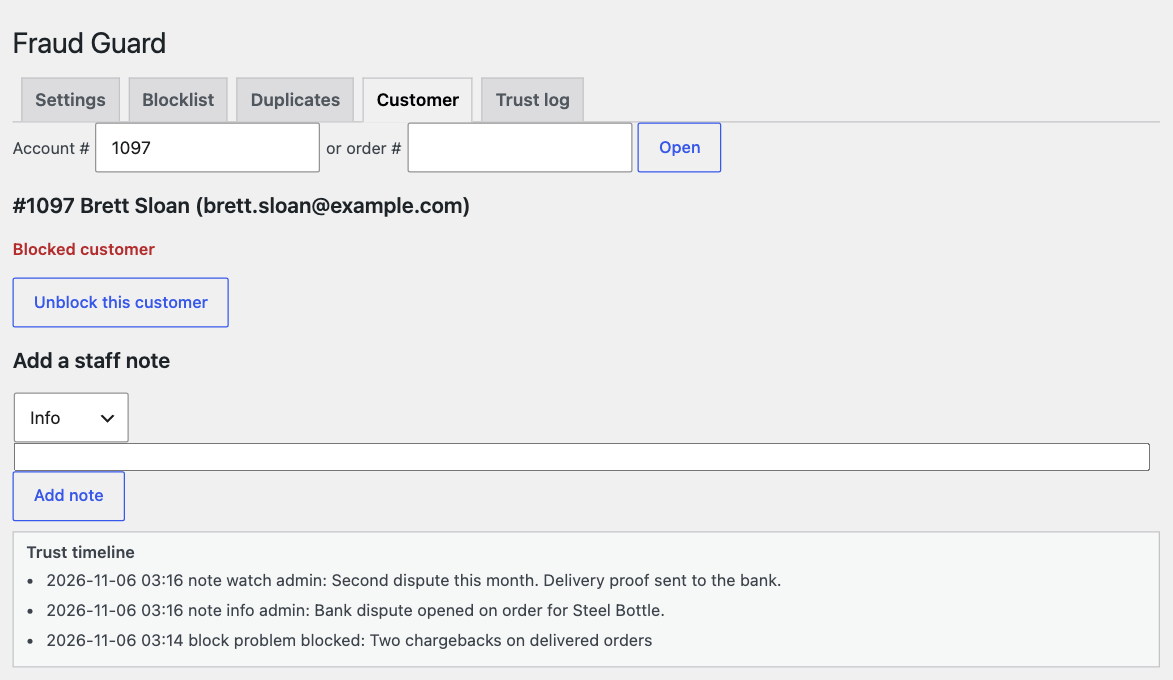
Links accounts that belong to one person. It compares the exact unit, the household, the network, a device cookie, the phone number (exact or one digit off), the email (same mailbox, similar name), and full name plus zip. Linked accounts form a family you can merge, un-merge and add staff notes to, with a queue for possible duplicates and a timeline for each customer. When you merge accounts, the main account’s owner is emailed. Signing in with a merged account’s password is off by default. If you turn it on, that password only opens the main account after its owner confirms through a single-use emailed link.
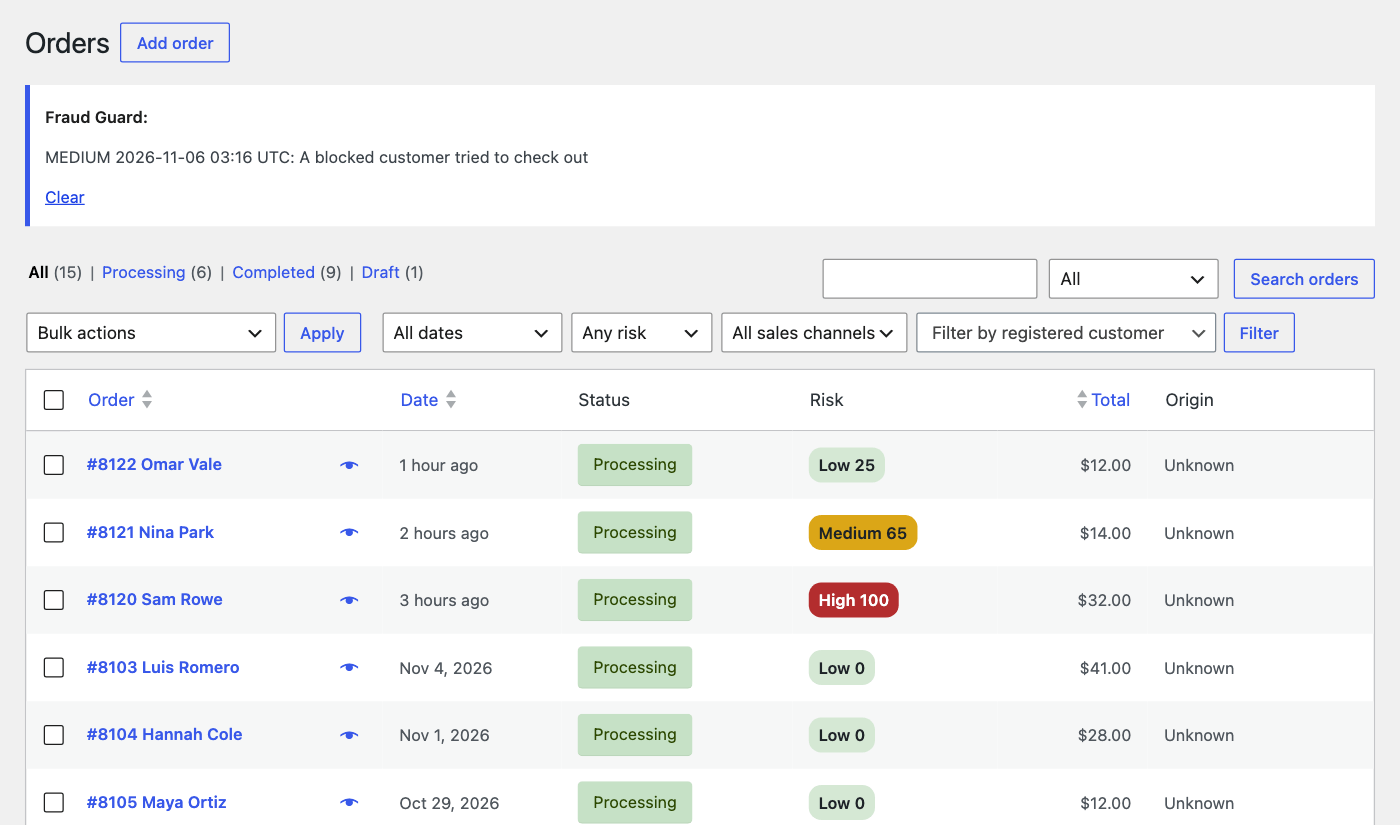
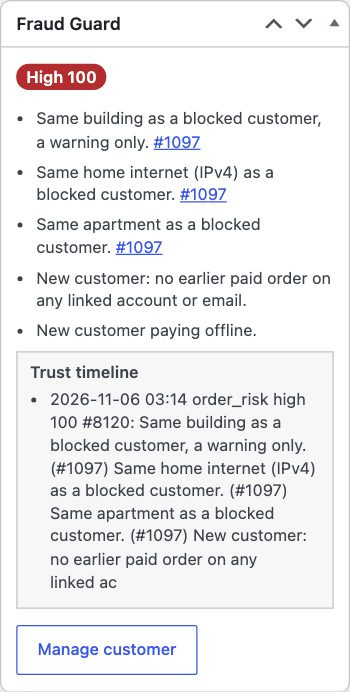
Scores every order. Each order gets a risk level (high, medium or low), a score from 0 to 100 and the reasons behind it. You see this in a column and filter on the orders list and in a box on the order. It also checks whether a “new customer” is really new, across the whole family and all their emails. You can choose to put risky orders on hold, add a note or send an alert.
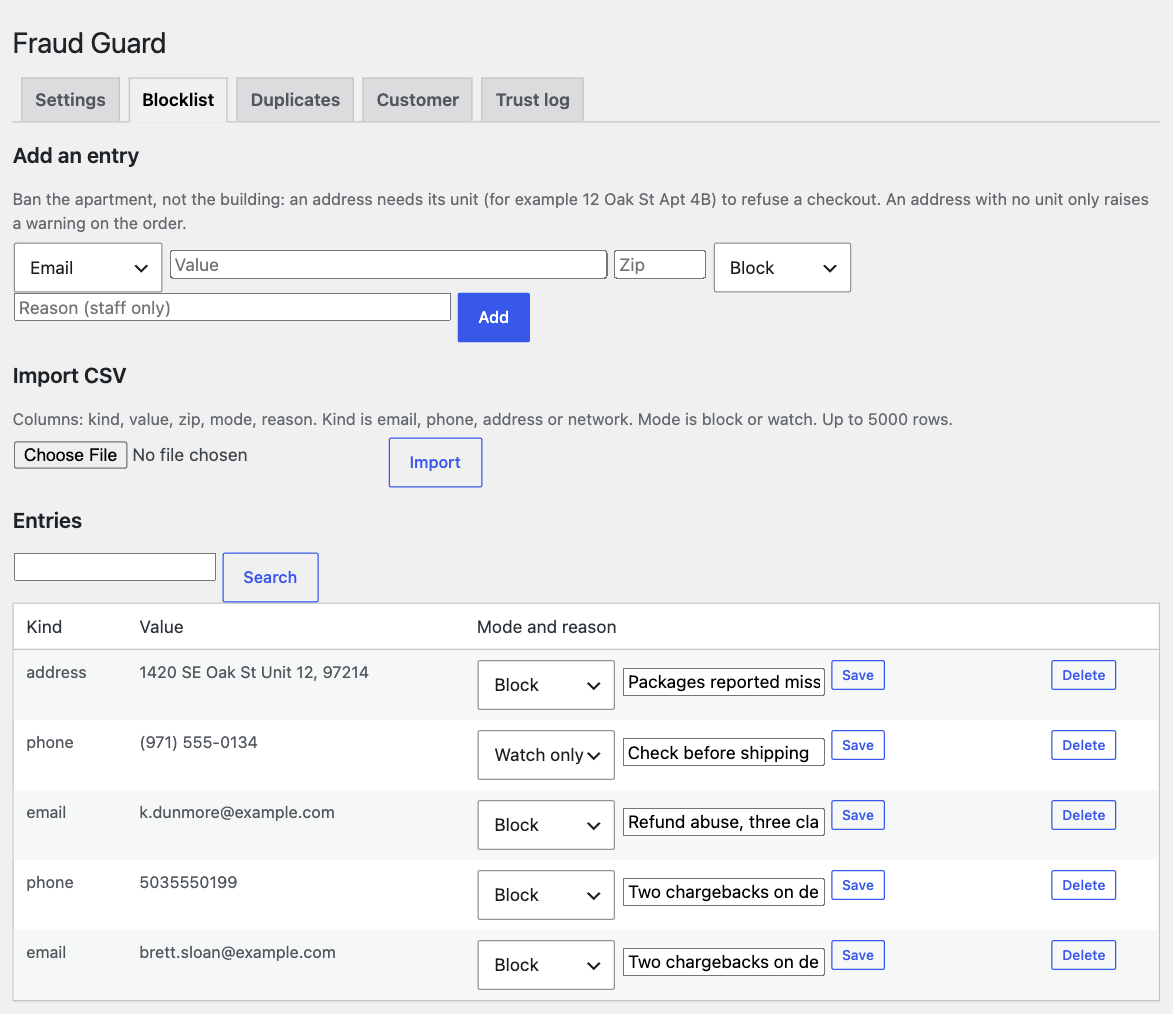
Gives you your own blocklist. Block or watch an email, phone, address or unit, or network. Add entries by hand or import a CSV.
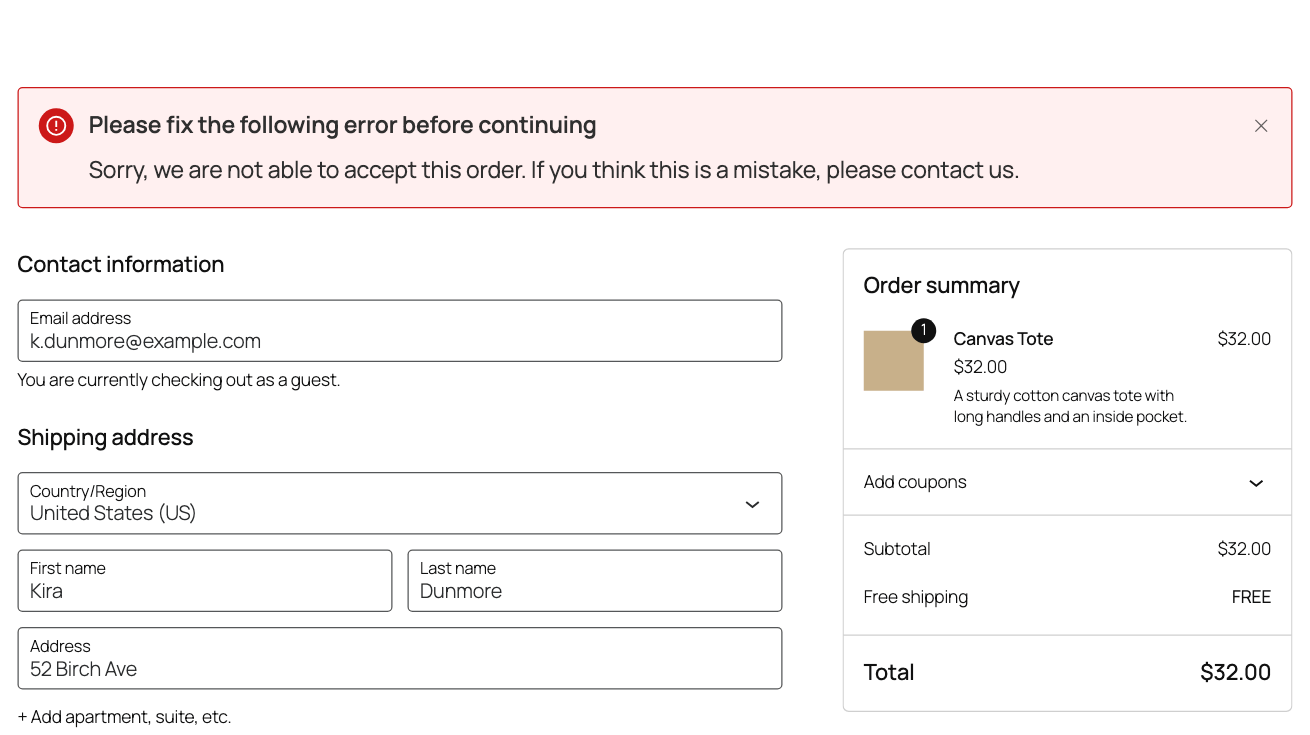
Refuses fake details at checkout. Numbers like 555-555-5555 and placeholder names and addresses are refused with a message you write. Every refusal is logged.
How it works at checkout
The checkout asks our server about the customer’s hashed details, and waits up to 3 seconds. An order is refused only on a strong match: a blocked account family, a blocklist hit, the exact email or phone of a blocked family, the same unit plus the same network, or the same device plus the unit or network. A shared building alone only raises a warning, so a neighbour can still buy.
Our server never blocks your checkout. If it is down or slow, the order goes through, your local blocklist and the fake detail checks still apply, and you see a notice in wp-admin. The order is checked again once the server is back.
Requirements
- WooCommerce 11.1 or newer, WordPress 6.5 or newer, PHP 8.1 or newer
- Works with HPOS on or off
- Works with block and classic checkout
Privacy: what leaves your store
What does not leave your store: raw names, emails, phone numbers, street addresses, zip codes, IP addresses, browser details, or plain customer and order numbers. The secret key used for hashing stays on your site and is never sent.
What goes to our server:
- Keyed hashes (HMAC-SHA256, with a secret that never leaves your site) of the customer’s email, phone, address, name, network and device.
- Customers appear only as keyed references.
- The house number and order ids, each shifted by a secret number for your store.
- The IP version.
- Dates of orders and refusals.
- Counts such as earlier paid orders, and merge and ban states.
- Yes or no flags: paid offline, disposable email domain, ID verified.
So this is not hashes alone, and those values are stored on our server. No raw names, emails, addresses, phones, IP addresses, user ids or order ids are sent.
The plugin also checks your licence about once a day. That check sends your licence key, store address, a site ID, and your plugin, WordPress, WooCommerce and PHP versions. Our server also sees your store’s IP address, and keeps it in its logs for up to 30 days.
How long we keep it: hashed records are deleted once they are 24 months old. Bans and blocklist entries stay until you remove them, because a ban should not quietly expire. If your licence stays inactive for 90 days, or you release a site from its licence for 90 days, all data for that store is deleted.
Each store’s data is kept separate on our server, so another store’s licence cannot read it.
Erasing data: the WordPress personal data eraser asks our server to delete a customer’s hashes. Uninstalling the plugin asks our server to delete your store’s data. Both requests still work after a licence lapses. A site released from its licence can no longer send them, so the 90 day rule above deletes that data instead. The same rule covers an uninstall request that does not arrive.
The trust log stays on your own site, holds the raw values, and has its own retention setting, exporter and eraser.
Pricing
1-year licence: $149. 3-year licence: $299. Lifetime licence: $359. Each is a one-time payment with no auto-renewal. When a 1-year or 3-year term ends, you buy a new licence to keep the plugin running.
Each licence covers one site.
What happens if you cancel
All features stop 7 days after your term ends. Your settings and data are kept, and a new licence restores everything.
- Keeps running: trust log retention and privacy erasers. If you turned merged login on, it stays on, so customers whose orders moved to a main account are not cut off.
- Stops: the fake phone and address checks, the whole blocklist, account matching, unit and network blocklist entries, the risk score, the orders column and box, new trust log entries, alerts, the duplicates and customer tabs, and the device cookie.
Honest limits
- Phone matching and fake phone checks cover the US and Canada only. Address matching needs a 5-digit postcode.
- Name matching looks at the exact first name, its first 3 letters, the exact last name, and one typo on last names of 5 or more letters. It does not catch initials or nicknames, so Mike and Michael do not match.
- Network matching uses the connecting address unless you pick a header in settings. Behind Cloudflare or another proxy, set it, or all shoppers look like one address.
- Without a geocoding plugin, “near a banned address” uses the same street and zip with a house number within 10. With one, it uses a grid of about 100 m, so a match can reach about 280 m and can be missed in rare cases.
- New accounts are not refused at sign-up, only at checkout. Orders created in admin or through the REST API are not scored at the time. They are only picked up by a backfill.
- The placeholder check can refuse a real address such as “123 Main St”. You can turn that check off.
- A customer who changes every detail will get through.
FAQ
Will it refuse real customers who share a building? A shared building alone only raises a warning. A refusal needs one of the strong matches listed above.
What about customers I already have? A background job sends your existing customers and orders as hashes the first time a licence is active, so matching starts with your history.
Does it work with any payment gateway? It looks at customer details and does not call your gateway. You can tell it which payment methods count as offline.
How is the risk score worked out? By fixed rules on our server: which details match, how strong the match is, and the order’s history. You see the reasons on every order.
Is there a free version? No. The plugin needs a licence: 1-year, 3-year or lifetime.

Reviews
There are no reviews yet.